Online Privacy and Marketplace Security: The Stash Patrick Perspective
Online privacy and marketplace security have become essential concerns in the modern digital economy. stash patrick Consumers now purchase products, transfer money, manage subscriptions, and access financial services through online platforms every day. While digital commerce offers speed and convenience, it also creates opportunities for criminals to target personal information, payment credentials, and online accounts.
The name “Stash Patrick” may appear in discussions involving underground marketplaces and payment-card related cybercrime. stashpatrick.cc Rather than treating such services as legitimate marketplaces, it is more useful to examine them from a cybersecurity perspective. The subject provides an opportunity to understand broader issues involving privacy, financial data protection, fraud prevention, and the security challenges facing online commerce.
Understanding Online Privacy
Online privacy involves controlling how personal information is collected, stored, processed, and shared. Almost every online activity can generate information, including shopping, banking, social media use, and account registration.
Some data collection is necessary for legitimate services. An online retailer needs delivery information to ship an order, while a financial institution needs certain details to provide banking services.
The important question is how organizations protect the information they collect. Poorly protected data can become a target for attackers, while excessive data collection can increase the potential consequences of a breach.
Consumers should therefore pay attention to what information websites request and whether the service has a legitimate reason for collecting it.
Marketplace Security and Consumer Confidence
Security is fundamental to the success of online marketplaces. Customers need confidence that their payment information and personal details are being handled responsibly.
Legitimate marketplaces generally use security controls such as encryption, authentication, fraud monitoring, access management, and secure payment processing.
When these protections fail, the consequences can be serious. A data breach may expose customer information, while payment fraud can result in direct financial losses.
Security incidents can also damage a company’s reputation. Customers may become reluctant to continue using a service if they believe their information is not adequately protected.
The Stash Patrick Perspective
References to Stash Patrick may appear in discussions about underground payment-card markets. Such environments should not be confused with regulated financial institutions, legitimate credit card providers, or established e-commerce services.
The broader cybersecurity lesson is more important than any specific marketplace name. Underground markets demonstrate how valuable payment information can become after it has been compromised.
Stolen card details may potentially be used for unauthorized transactions or combined with other personal information to facilitate additional forms of fraud.
Consumers should never purchase payment credentials, financial accounts, or personal information from unauthorized sources. Such activity can expose individuals to scams, malware, identity theft, financial losses, and legal consequences.
How Personal Information Becomes Compromised
Personal and financial information can be exposed through several attack methods.
Phishing remains one of the most common techniques. Attackers may impersonate banks, retailers, delivery services, or payment providers and attempt to persuade victims to disclose passwords, card information, or verification codes.
Data breaches are another major source of compromised information. Criminals may target organizations that store large quantities of customer data.
Malware can also affect computers and mobile devices. Some malicious programs are designed to steal credentials or monitor user activity.
Social engineering is equally important because attackers can exploit trust, urgency, or fear to manipulate people into making unsafe decisions.
Why Financial Privacy Matters
Financial information is particularly sensitive because unauthorized access can have direct economic consequences.
A stolen card number may result in fraudulent purchases. Compromised banking credentials may allow unauthorized account access. Personal information can also be combined with other data to support identity-related fraud.
Protecting financial privacy therefore requires more than simply hiding information. Organizations need to ensure that sensitive data is accessed only by authorized users and processed for legitimate purposes.
Consumers should also understand that sharing information unnecessarily can increase their exposure to potential fraud.
Strong Authentication
Authentication is a central component of online security.
Passwords remain common, but relying solely on passwords can create significant risks. If a password is stolen through phishing or a data breach, an attacker may attempt to reuse it elsewhere.
Multi-factor authentication provides an additional security layer. It can require a second verification method, such as an authentication application, security key, or biometric factor.
Consumers should enable multi-factor authentication for financial and other sensitive accounts whenever available.
Businesses should also implement stronger authentication for employees, administrators, and users with access to sensitive systems.
Payment Security Technologies
Modern payment systems use several technologies to protect transactions.
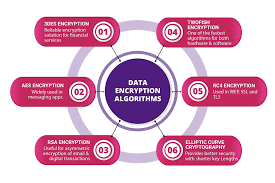
Encryption can help secure information while it moves between systems. Tokenization can reduce the exposure of actual card information by replacing sensitive details with alternative values during supported transactions.
Financial institutions also use fraud detection systems to identify unusual behavior. These systems may evaluate transaction patterns, account activity, device characteristics, and other signals.
Artificial intelligence and machine learning can assist in analyzing large volumes of transaction data and identifying patterns that may indicate fraud.
However, security technology works best when combined with responsible user behavior.
Recognizing Suspicious Online Services
Consumers should be cautious when websites or online communities offer financial credentials, payment accounts, or card information at unusually low prices.
Legitimate financial providers do not sell stolen credit card information or unauthorized accounts.
Other warning signs can include requests for unnecessary personal information, pressure to use unusual payment methods, claims of guaranteed access to financial accounts, or instructions that require users to bypass normal security procedures.
Consumers should avoid such services and obtain financial products directly from legitimate and regulated providers.
Protecting Personal Accounts
Individual users can take several practical steps to strengthen online privacy.
Using a unique password for each important account can reduce the impact of credential theft. A password manager can help users manage complex passwords without having to memorize each one.
Multi-factor authentication should be enabled whenever possible.
Transaction notifications can also help consumers identify suspicious purchases quickly. Regularly reviewing bank and credit card statements provides another opportunity to detect unusual activity.
Consumers should also keep operating systems, browsers, and applications updated to reduce exposure to known security vulnerabilities.
What Businesses Can Do
Businesses need a comprehensive approach to marketplace security.
Access to sensitive information should be restricted according to job responsibilities. Employees should not automatically receive access to financial or customer information that they do not need.
Organizations should regularly update software, conduct security assessments, monitor systems, and address vulnerabilities.
Employee education is another essential component. Staff should understand phishing, social engineering, suspicious attachments, fraudulent login pages, and other common attack techniques.
Businesses should also maintain an incident-response plan so that suspicious activity can be investigated quickly.
Data Minimization
Data minimization is another important privacy principle. Organizations should avoid collecting information that is not necessary for legitimate business purposes.
The less unnecessary information a company stores, the less information could potentially be exposed during a breach.
Businesses should also establish retention policies and securely dispose of information that is no longer required.
These practices can reduce both privacy risks and the potential impact of cybersecurity incidents.
The Future of Marketplace Security
Online marketplace security will continue to evolve. Artificial intelligence, behavioral analytics, tokenization, biometric authentication, automated monitoring, and stronger identity verification are likely to play increasingly important roles.
At the same time, cybercriminals will continue adapting their techniques. They may target human behavior through increasingly convincing phishing campaigns or attempt to exploit vulnerabilities in software and third-party services.
For this reason, cybersecurity cannot be treated as a one-time project. Businesses and consumers need to continuously review their security practices.
Conclusion
Online privacy and marketplace security are critical to maintaining trust in the digital economy. References to Stash Patrick and similar underground marketplace names highlight the risks associated with stolen payment information and financial cybercrime.
The most useful lesson is not how to interact with underground markets, but how to protect against the threats they represent.
Consumers can strengthen their security by using unique passwords, enabling multi-factor authentication, monitoring transactions, protecting personal information, and avoiding suspicious financial services.
Businesses can reduce risk through secure payment systems, access controls, employee training, data minimization, vulnerability management, monitoring, and effective incident-response planning.
As digital commerce continues to expand, protecting financial and personal information will remain a shared responsibility. A combination of strong technology, responsible data practices, consumer awareness, and continuous security improvement can help create a safer and more trustworthy online marketplace environment.